

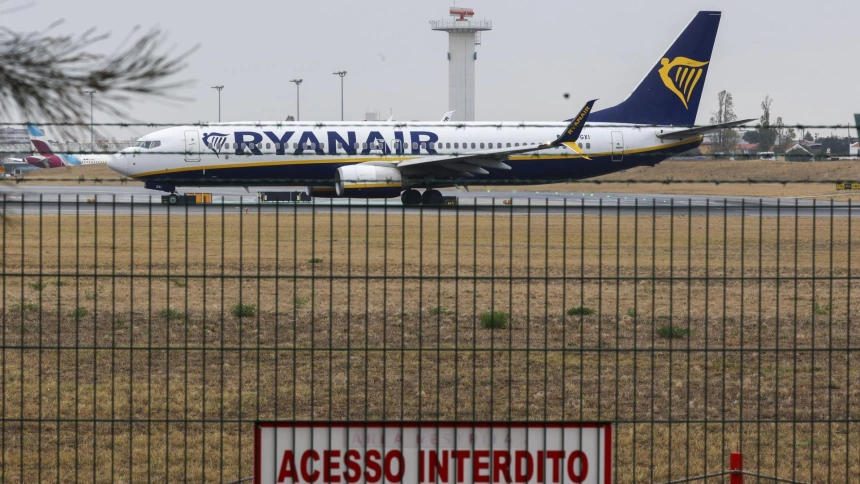
Recent fake bomb threats targeting passenger flights could be tests designed to probe European defenses ahead of more severe attacks, cybersecurity researcher Josep Albors warned.
Albors, the head of research at cybersecurity firm ESET, said that while such incidents could technically be an enormous prank, the broader geopolitical environment strongly points toward a coordinated campaign of hybrid warfare.
Speaking on the evening radio show La Linterna on Spain's COPE network with host Angel Exposito, the specialist explained that hostile actors may be attempting to destabilize European society while quietly mapping how emergency services respond.
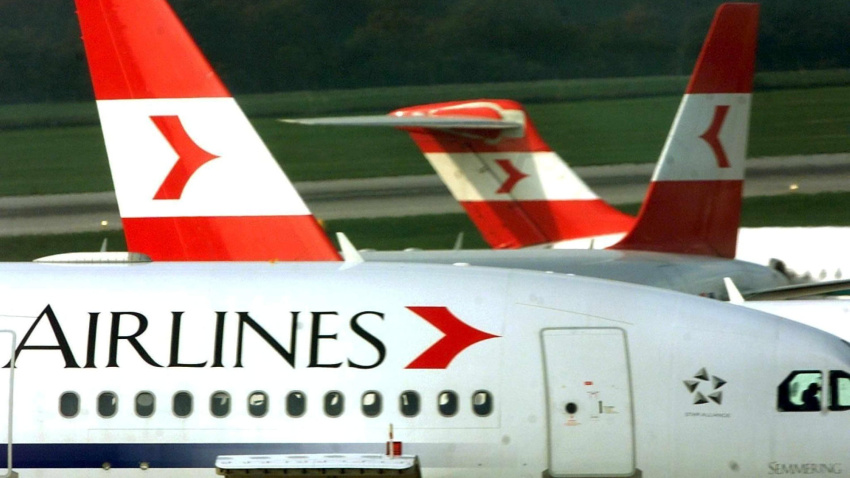
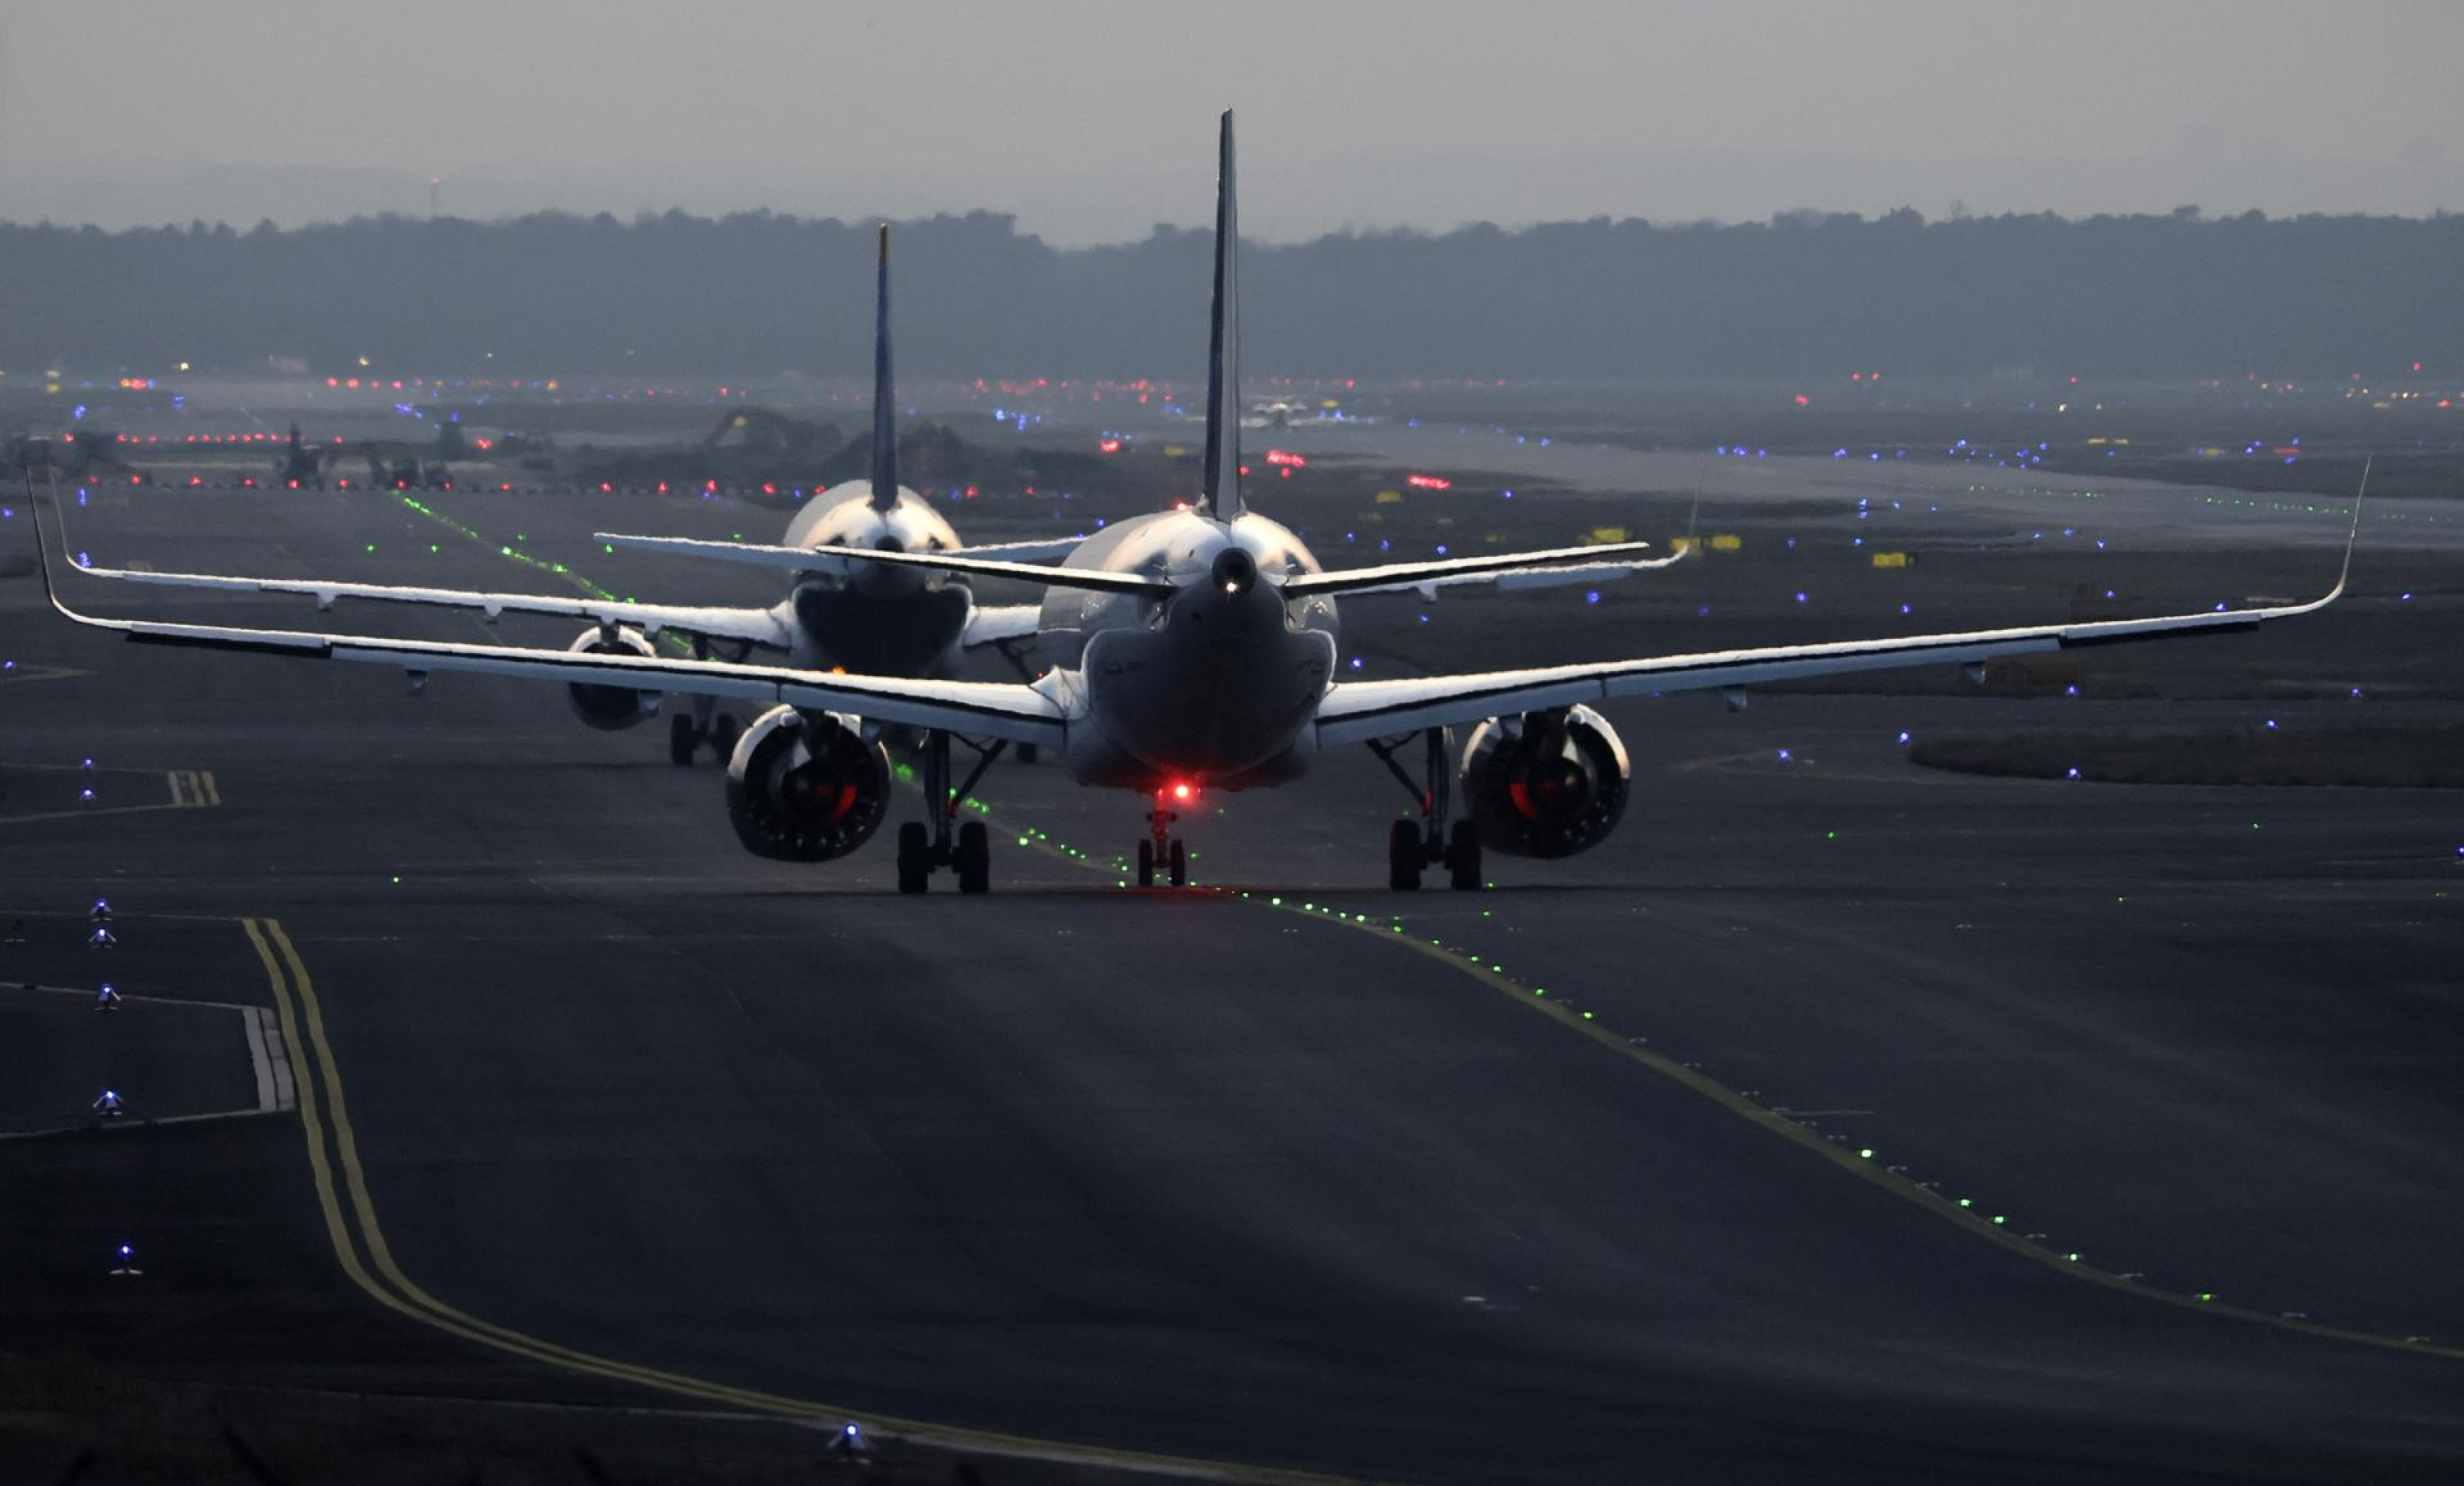
The warning follows a string of aviation security alerts, including an Austrian Airlines flight traveling from Tel Aviv to Vienna that had to make an emergency diversion to Sofia on Sunday. Bulgarian authorities searched the aircraft and found no explosives or hazardous materials before releasing the plane to land in Vienna early Monday.
At the same time, cyberattacks have struck public infrastructure and commercial networks across the continent, including an incident in Moldova that affected 450,000 citizens.
When asked why cybercriminals and hostile groups carry out these disruptive operations, Albors said the simplest explanation is that they do it because they can. Attackers look for internet-connected systems left exposed to the public web, search for unpatched software flaws, and exploit them.
Albors noted that the rapid rise of artificial intelligence has made these operations far easier to execute than in previous years, giving perpetrators automated tools to scan networks and craft deceptive messages. However, tracing the true culprits remains extremely difficult. He stressed that investigators can never be completely certain of attribution because malicious actors frequently stage false-flag operations to pin the blame on others.
Hybrid warfare and airline disruption
The pattern of recent disruptions has raised alarms across European security circles. Albors argued that while investigators must technically consider the possibility of reckless mischief, geopolitical realities give far more weight to state-sponsored pressure.
According to the ESET researcher, two main scenarios are currently on the table, and both can operate simultaneously. Attackers may seek to cause public alarm and sow instability in Western nations, or they may be conducting reconnaissance to see how quickly aviation authorities, intelligence agencies, and police forces react.
Such probing allows adversaries to identify reaction times, protocols, and vulnerabilities before preparing a far more serious physical or digital strike in the future.
In modern military strategy, hybrid warfare combines cyber operations, digital harassment, and psychological pressure with conventional tactics. By keeping attacks beneath the threshold of open military conflict, perpetrators aim to drain resources and test defenses without provoking a direct military response.
The diversion of the Austrian Airlines Boeing jet to the Bulgarian capital of Sofia demonstrated the immediate real-world costs of these tactics. Under international aviation safety rules, commercial airlines and air traffic controllers must treat every bomb warning as an active emergency, forcing aircraft to divert, dump fuel, and undergo hours of intense security checks on the ground.
Vulnerabilities in critical infrastructure
Aviation is not the only sector facing disruption. Digital saboteurs have increasingly targeted commercial supply chains and civilian infrastructure that rely on automated control systems.
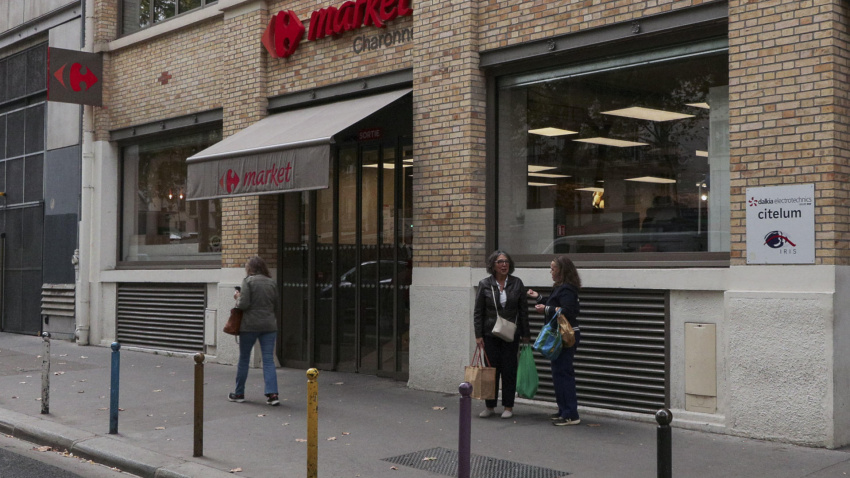
In France, a cyberattack targeted the cooling systems of Carrefour supermarkets in Paris, leaving food retailers with damaged stock. According to affected businesses, the sabotage of commercial refrigeration units spoiled perishable food worth tens of millions of euros.
Carrefour, one of the world's largest grocery retailers, operates thousands of stores across Europe. Industrial control systems that manage temperature, power, and logistics are increasingly connected to company networks, creating fresh avenues of attack for digital saboteurs.
Albors warned that system vulnerability is no longer a future danger but a reality that has already arrived. He stated that any company with an exposed attack surface that fails to patch vulnerabilities and install security updates is at risk of being breached.
The problem is compounded in countries bordering conflict zones. In Moldova, a former Soviet republic located between Romania and Ukraine, recent cyber interference affected 450,000 citizens, highlighting how regional instability spills over into civilian digital networks.
European regulation and implementation gaps
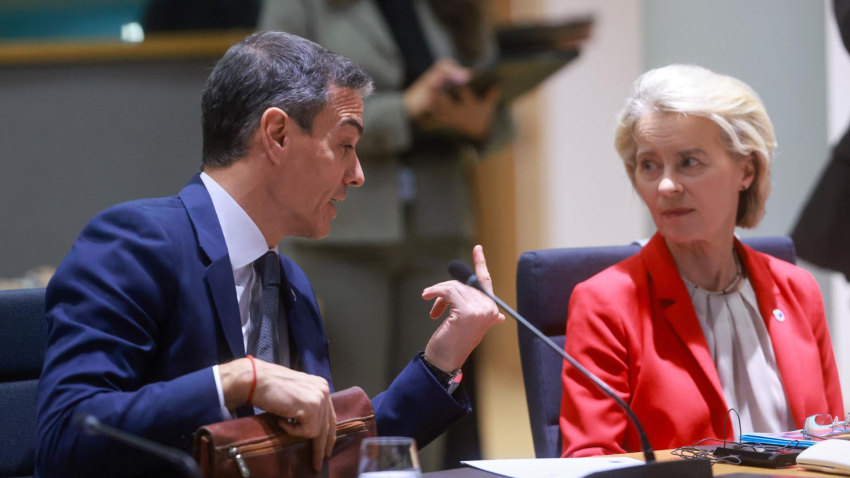
The surge in digital aggression has prompted debate over whether Europe is adequately prepared to defend its networks. European Commission President Ursula von der Leyen and Spanish Prime Minister Pedro Sanchez have repeatedly prioritized digital security and resilience across the European Union.
Albors made a sharp distinction between the continent's legal frameworks and their execution on the ground. He praised European regulatory standards as adequate, but warned that practical application remains a severe problem across Europe and the wider world.
While strict rules exist on paper to protect critical services, organizations often struggle to translate statutory mandates into day-to-day defenses.
The researcher identified two main reasons for this implementation gap: a lack of general awareness and limited financial budgets. He noted that members of the public and corporate executives often assume nothing is wrong unless major incidents appear in news headlines, even though cybersecurity analysts witness malicious activity every single day.
Furthermore, many commercial enterprises continue to view cybersecurity as an inconvenient expense rather than a vital investment necessary for business survival. As the sabotage of supermarket refrigeration units in France showed, neglecting digital defenses can quickly wipe out tens of millions of euros in inventory.
Foundational defenses and public vigilance
To counter mounting threats, Albors emphasized the crucial role of technical specialists and cybersecurity companies that provide actionable intelligence alongside defensive software. He pointed to the work of Spain's National Centre for Critical Infrastructure Protection, known as CNPIC, which coordinates defense strategies for essential services across the country.
CNPIC works under the Spanish Ministry of the Interior to oversee security in key sectors, including energy, transport, banking, healthcare, and water supply, ensuring that both physical sites and digital systems meet rigorous protection benchmarks.
Albors concluded that media coverage is a necessary first step to ensure people remain vigilant and understand that hybrid threats are active. From that baseline of awareness, institutions and private businesses must focus on implementing core security practices that have proven their worth over decades, building solid foundations rather than chasing expensive or overly complex tools.


